
Action: launch a Nessus scan#
Start a Nessus scan automatically after a node is scanned. For example, with a Nessus integration, you could trigger a Nessus scan after a 'Node Scanned' event to obtain a complete picture of the node's state at that point in time. Once the Nessus scan is complete, you can then view the results directly in Guardian.
Applies to: Guardian Classic
Note
The following process assumes you have a Nessus integration already configured in Guardian. For more information, see Nessus Integration.
Tip
For an overview of actions in Guardian, including more options available to choose from, see Actions.
Action Settings#
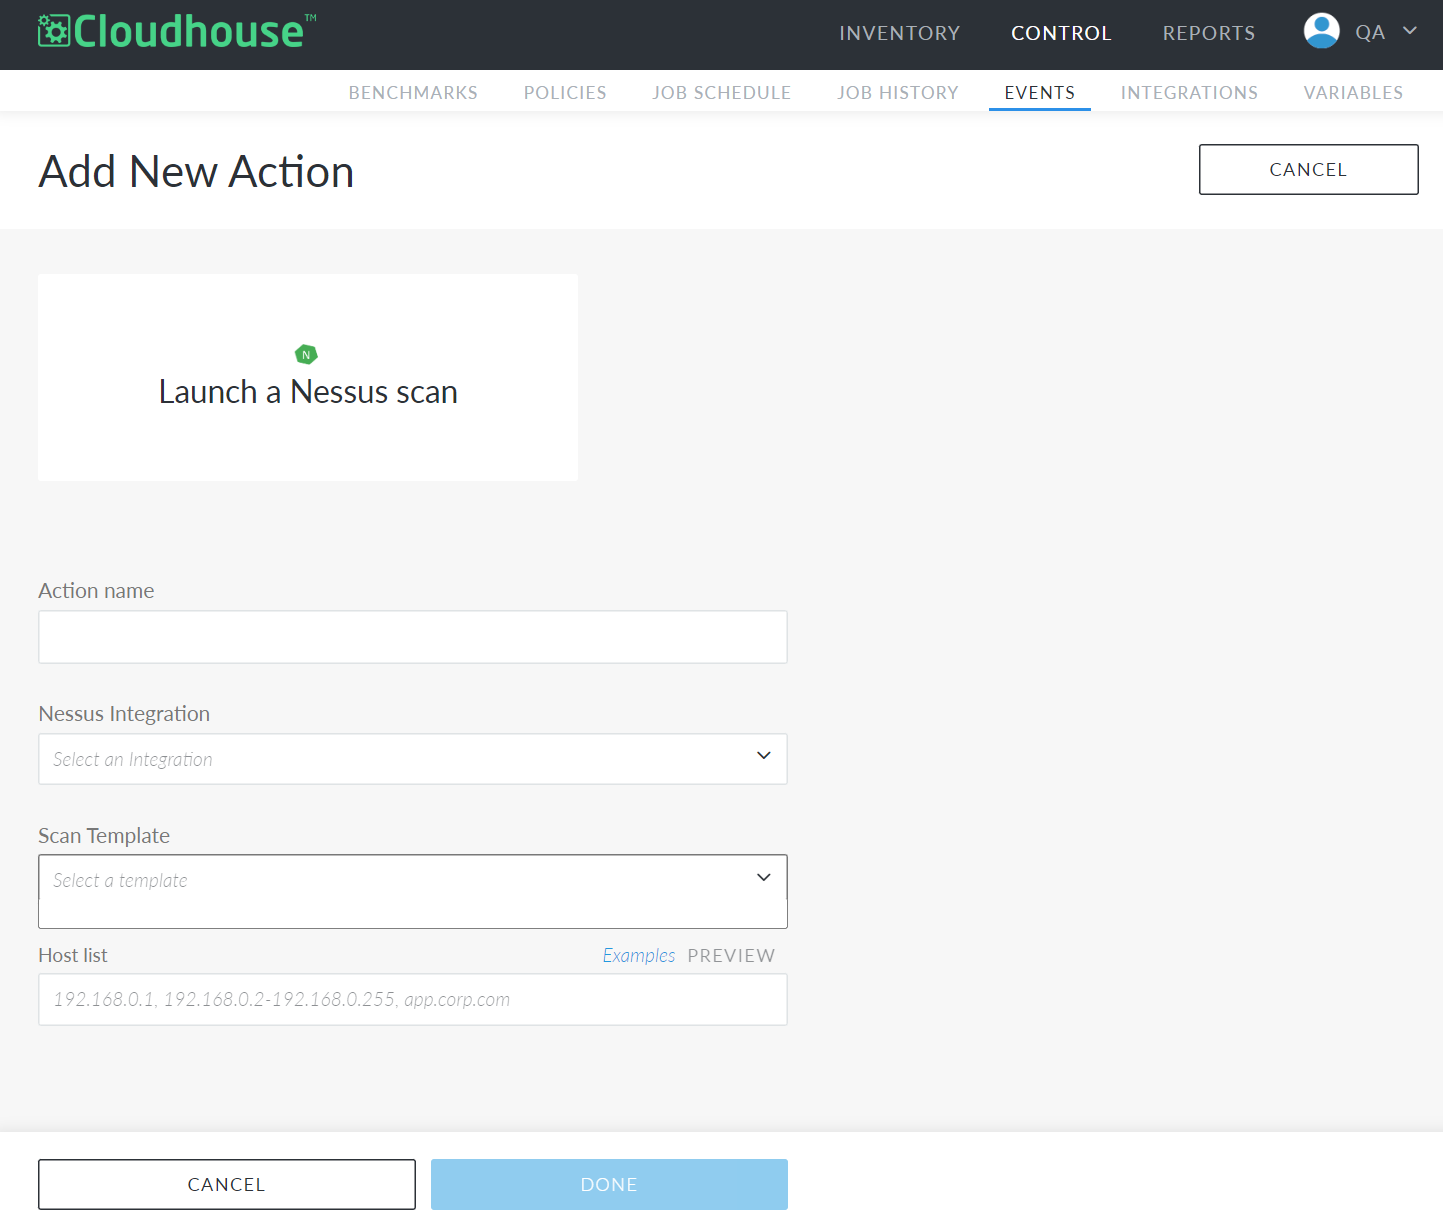
When configuring a Launch a Nessus scan action, the following settings are presented:
- Action name field
- A unique name for the action. This name is how you will identify this action among all others configured in your Guardianinstance, so ensure it is descriptive. For example, 'Node Scanned Nessus Scan' and not simply 'Nessus Scan'.
- Nessus Integration drop-down list
- A list of all Nessus integrations configured in your Guardian instance. From the drop-down, select the integration where you want to run scans triggered by this action.
- Scan Template drop-down list
- A list of all the scan templates available in your selected Nessus integration. Nessus scan templates are pre-configured checks Nessus runs against your systems. For example, you could have Discovery, Vulnerabilities, or Compliance scan templates, each of which verify different configurations across your devices. From the drop-down, select the scan template you want to run when this action is triggered.
- Host list field
- The nodes (known as hosts in Nessus) you want to scan when this action is triggered. Here, you can enter the variable
{{ node }}to automatically scan the node that triggered the action.
These settings are configured when adding a new action, and they can also be edited at any time through the Actions tab (Control > Events > Action). To edit an action from the Actions tab, click the Ellipsis ( ) and select Edit. Once you have made your edits, click Done to save them.
Add a launch a Nessus scan action#
You can add a new Launch a Nessus scan action from any saved view in your Guardian instance. Each saved view represents a specific event determined using a query on the Events page. The saved view you select during this configuration determines the corresponding event that triggers your new action. For more information, see Saved Views.
To add a Launch a Nessus scan action, complete the following process:
Tip
For help completing any of the following fields, refer to their respective descriptions in the Action Settings table above.
- Navigate to the Events tab (Control > Events).
-
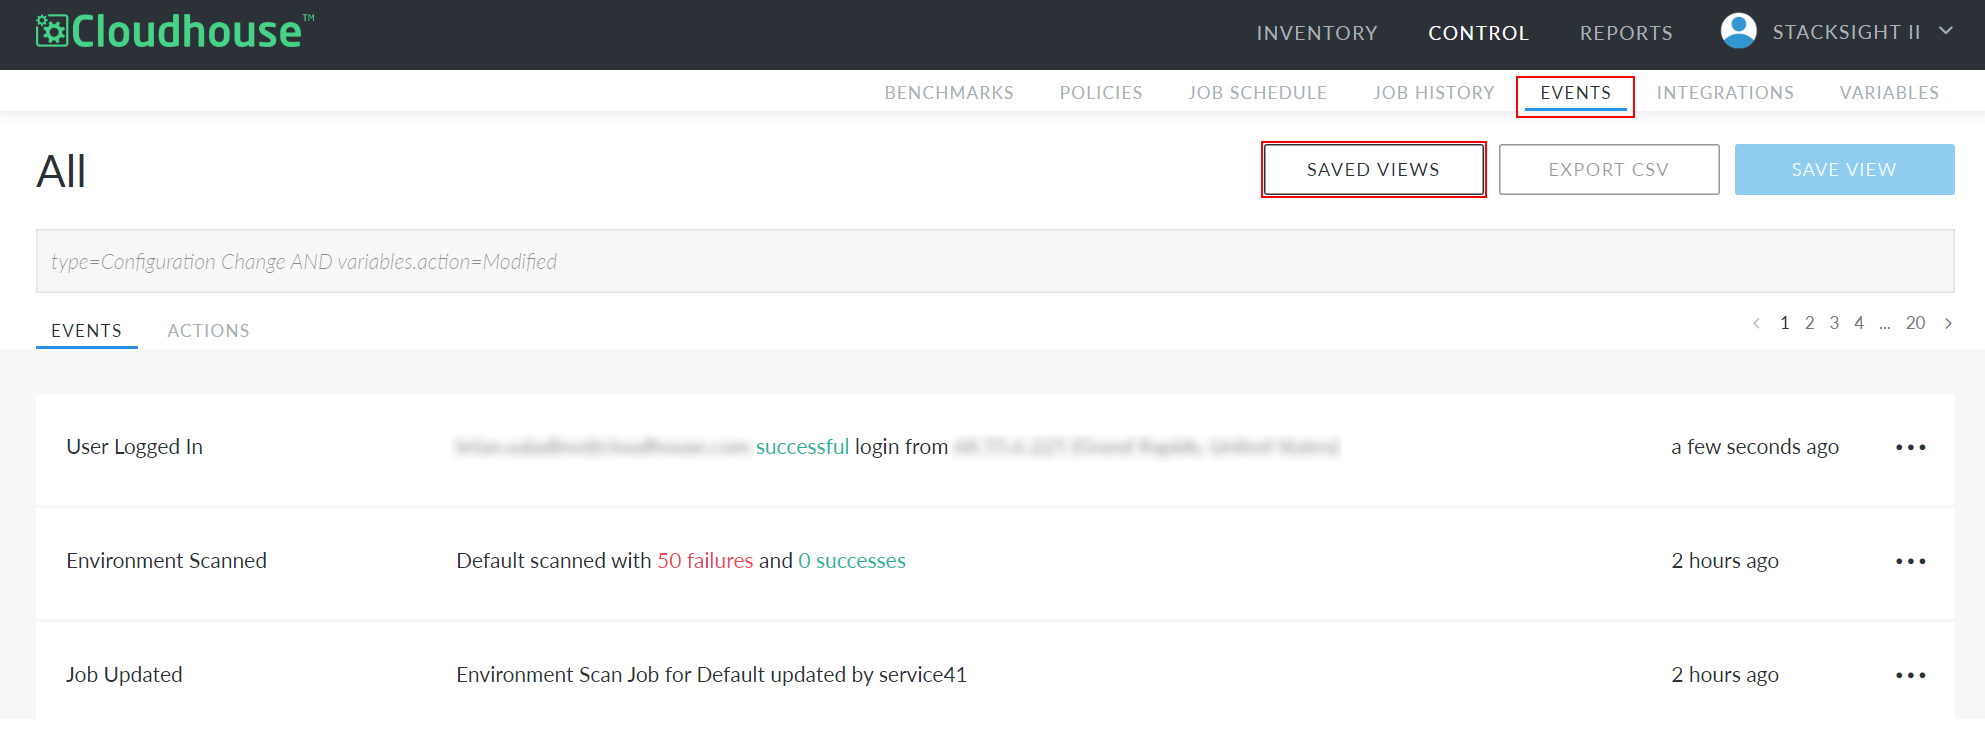
Click the Saved Views button at the top of the page. The Saved Views side panel is displayed.
-
Select the event you want to trigger your new action. The saved view for that event is displayed.
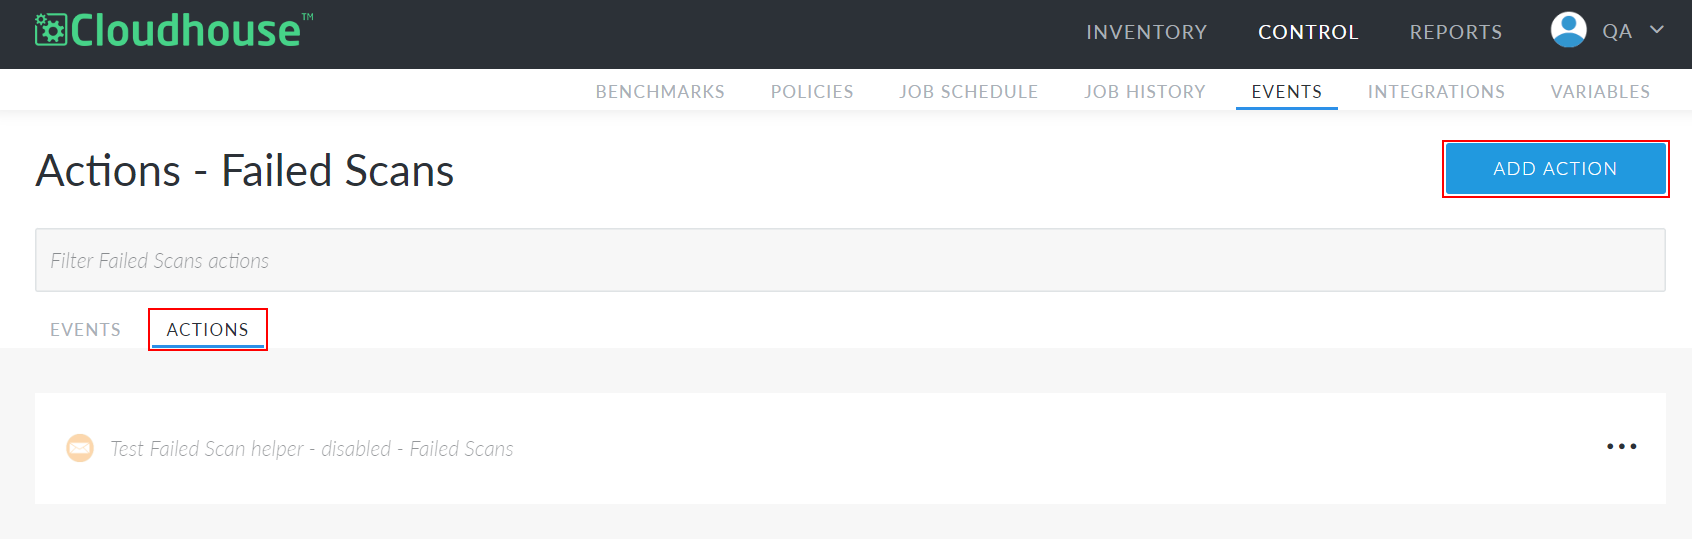
- Click the Actions tab to display all existing actions configured for this event.
-
Click the Add Action button. The Add New Action page is displayed.
-
Click Launch a Nessus scan. The required fields are displayed.
- Enter an Action Name.
- Select an integration from the Nessus Integration drop-down list.
- Select a Nessus scan to perform from the Scan Template drop-down list.
- Enter a node or nodes to scan in the Host List field. This can be a variable such as
{{ node }}to automatically scan the relevant node. - Click Done.
Now, a confirmation dialog is displayed and you are redirected to the Actions tab for your selected saved view. Here, you can view your new action. To disable, edit, or test the action, click the Ellipsis () and select the appropriate option.
View Nessus scan results#
After a Nessus scan is complete, a new event will be displayed on the Events page in Guardian. You will see an 'External Vuln Scan Complete' event for each scan triggered by your action:
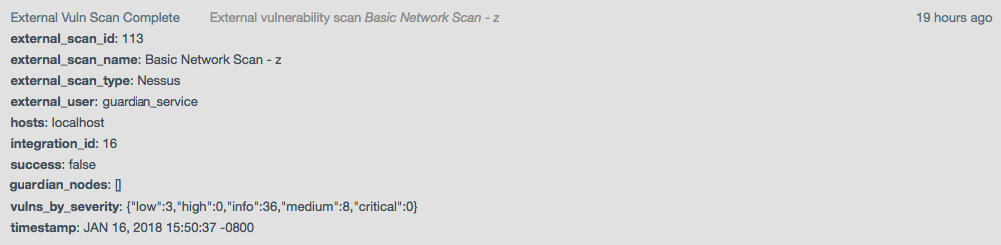
This event contains the following fields:
- external_scan_id
- The scan number as it is referenced within Nessus.
- external_scan_name
- The scan name as it is referenced within Nessus.
- external_scan_type
- The service that ran the scan. In this case, this value will always be 'Nessus'.
- external_user
- The username of the Nessus account used to perform the scan. This value corresponds with the Username you designated when configuring your Nessus integration.
- hosts
- The hosts Nessus attempted to scan.
- integration_id
- The internal ID used by Guardian to identify the integration used to trigger the scan.
- success
- A boolean value indicating whether the Nessus scan was successful.
- guardian_nodes
- A list of node IDs that correspond to the hosts scanned by Nessus.
- vulns_by_severity
- The number of vulnerabilities detected during the scan, categorised by severity.
- timestamp
- The date and time the scan occurred.